目录7 个章节
The short answer to how banks control AI agents: they separate what an agent can see from what it can do. As of October 2026, the largest US banks block outside AI agents from logging in with a customer's password and moving money, while still allowing read-only data access through approved open banking connections. For their own internal agents, banks layer narrow permission scopes, audit logs that record agent actions, and human approval at the points where money leaves an account. This guide is based on reporting and regulator documents checked through November 2, 2026, and covers US banks first, with South Korea's rules for comparison.
Why banks control AI agents now: what happened in October 2026
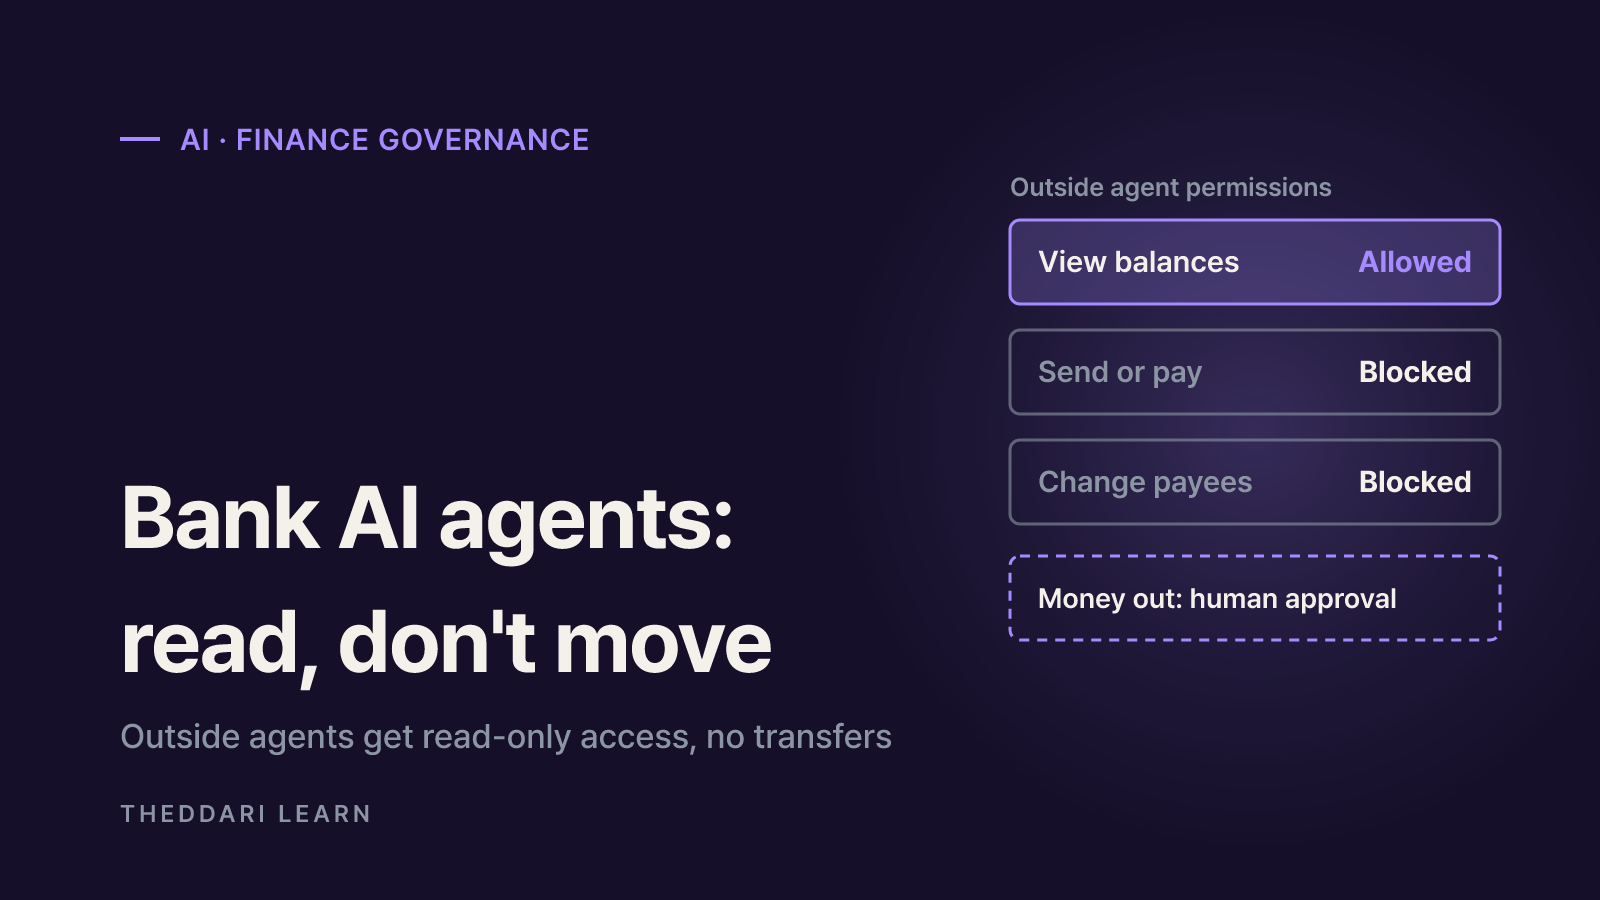
Consumer agents such as Meta's Muse and OpenAI's Dots went mainstream in the fall of 2026, and some customers began handing them their bank credentials. On the bank's third-quarter earnings call on October 13, JPMorgan Chase CEO Jamie Dimon said the bank would not let "just any outside agent" inside, warning about rogue agents that "could be thousands of them," according to CNBC. A spokeswoman confirmed JPMorgan does not permit third parties to log in with customers' banking credentials, but supports customer-authorized data sharing through open banking providers. In practice, an agent can read balances through a connector like Plaid but cannot send money or pay a bill.
By October 27, American Banker reported that five of the largest US banks, JPMorgan Chase, Citi, Bank of America, Wells Fargo and Morgan Stanley, were blocking external agents from customer accounts, and that Charles Schwab was blocking Muse and similar tools. The same article described an unnamed large bank that watched an ordinary-looking agent reset a password, change the approved transfer accounts and move $100,000 out. PYMNTS reported that Bank of America CEO Brian Moynihan said a human should stay in the loop to approve money moving out of an account, and that Schwab blocks unauthorized agents a double-digit number of times every week.
The four controls banks use on AI agents
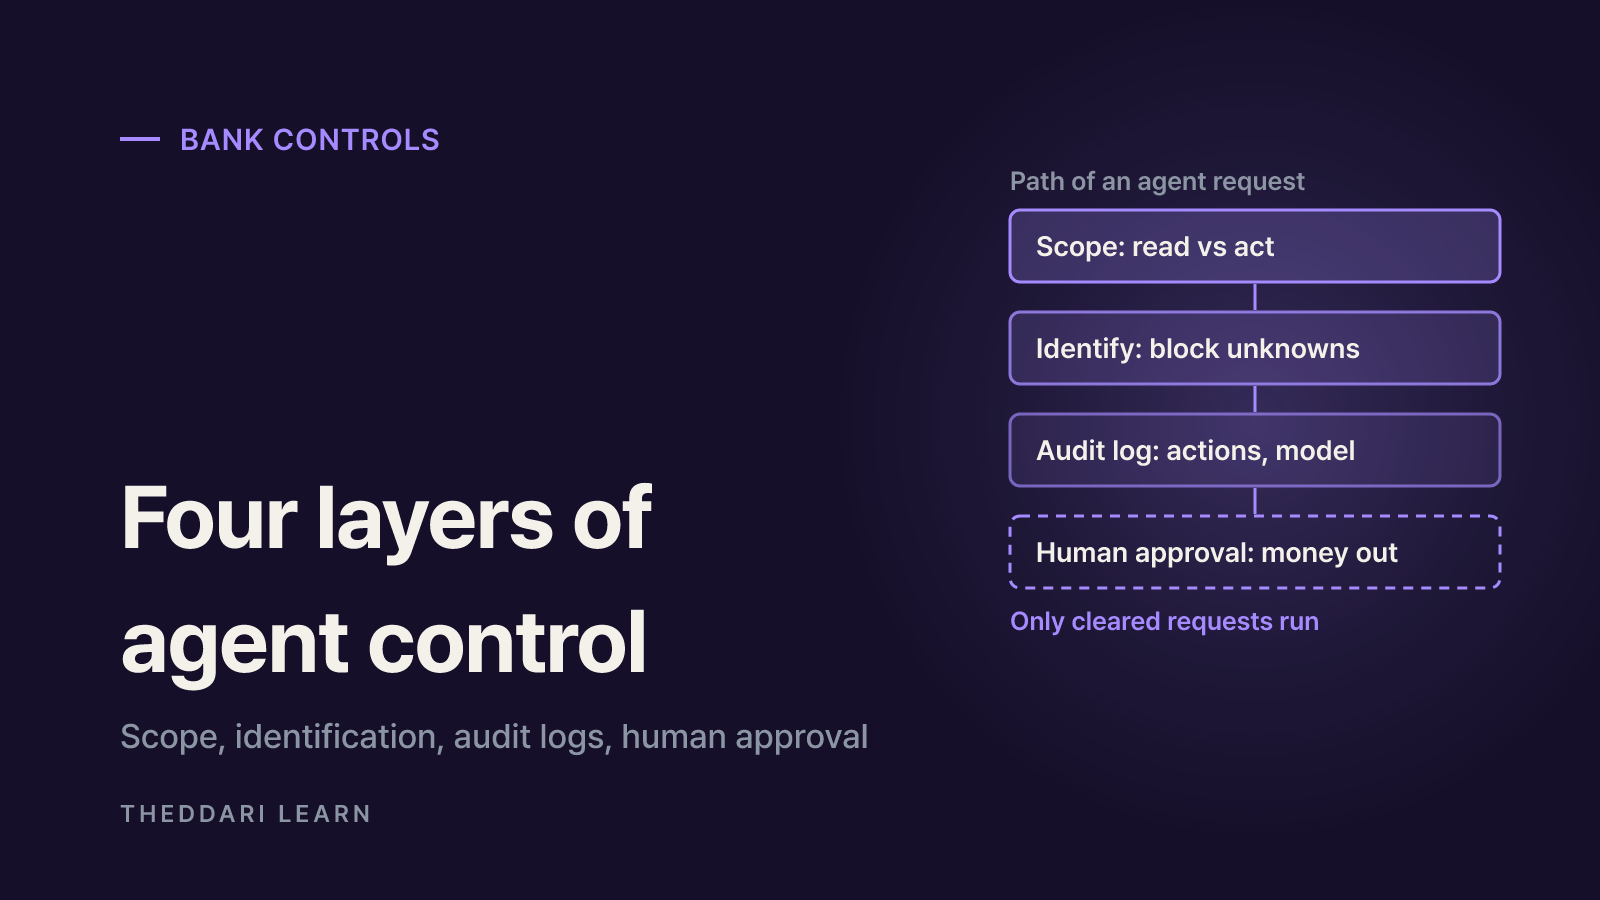
Banks rarely publish their internal playbooks, but the same four controls show up across executive comments and supervisory documents. As M&T Bank's head of AI risk put it to American Banker, a bank needs to know what is accessing its environment, what permissions it has and what actions it could take. The table maps those questions to controls.
Permission scope
- What it governs
- Whether an agent can only read or can also act
- How it shows up at banks
- Outside agents get read-only access; transfers, payments and payee changes are blocked
Audit logs
- What it governs
- Tracing who did what, and when
- How it shows up at banks
- Prompt and output logs, model version tracking, agent action and decision records
Human approval
- What it governs
- Final say on hard-to-reverse actions
- How it shows up at banks
- A person approves when money leaves the account
Identification and blocking
- What it governs
- Access by agents of unknown origin
- How it shows up at banks
- Blocking self-identifying agents, monitoring unusual behavior
Permissions: read versus act
The biggest line is between read and write access. An agent that misreads a balance produces a bad summary; an agent with transfer rights that gets it wrong loses money. FINRA's 2026 Annual Regulatory Oversight Report lists "scope and authority" as a core agent risk: agents may act beyond the user's actual or intended authority. That is why banks split viewing, transferring and editing payees into separate permissions and shut off the riskiest ones first.
Audit logs: making multi-step reasoning traceable
FINRA warns that complicated, multi-step agent reasoning can make outcomes difficult to trace or explain. Its suggested practices include storing prompt and output logs, tracking which model version was used and when, and tracking agent actions and decisions. Without that trail, a bank cannot tell after an incident whether a transfer came from the customer's instruction, the agent's own planning, or an attacker.
Human approval: placed where mistakes are hard to undo
Putting a person on every step would defeat the point of automation, so banks target the irreversible moment. PNC CEO William Demchak said agent transactions inside accounts would require secure connections, authentication and human-in-the-loop controls, plus new laws on liability shifting.
Where regulation stands: US and South Korea
A notable gap: the main US supervisory guidance on model risk does not yet cover agentic AI. The revised interagency guidance issued April 17, 2026 (OCC Bulletin 2026-13) by the OCC, the Federal Reserve and the FDIC replaced the 2011 SR 11-7 framework, but states that generative AI and agentic AI models are novel and rapidly evolving and therefore outside its scope. The guidance is most relevant to banks with over $30 billion in total assets and sets no enforceable standards. The agencies said they plan to issue a request for information that specifically considers banks' use of generative and agentic AI.
Key documents
- United States
- Interagency model risk guidance (April 2026); FINRA 2026 oversight report
- South Korea
- FSC guidelines on AI in the financial sector (effective June 22, 2026)
Treatment of agents
- United States
- Model risk guidance excludes agentic AI; FINRA lists agent risks separately
- South Korea
- Revision reflects the arrival of AI agents; rules on agent authority still under review
Role of humans
- United States
- FINRA suggests deciding where human-in-the-loop oversight applies
- South Korea
- Assistive-tool principle: staff make final decisions and bear responsibility
Legal force
- United States
- Guidance is non-binding; violations of existing law remain actionable
- South Korea
- Self-regulatory, but high-impact AI under Korea's AI Framework Act carries legal duties
In South Korea, the Financial Services Commission announced on June 18, 2026 revised guidelines built on seven principles: governance, legality, use as an assistive tool, reliability, financial stability, good faith and security. The assistive-tool principle treats AI as support for staff, with final decisions and accountability kept with employees. The Financial Supervisory Service released an AI risk management framework and the Financial Security Institute a security guide alongside it. The FSC said that because agents may soon recommend products, sign customers up and make payments, it will review rules covering agent authority and responsibility, then test services in a regulatory sandbox.

What customers should check before connecting an agent
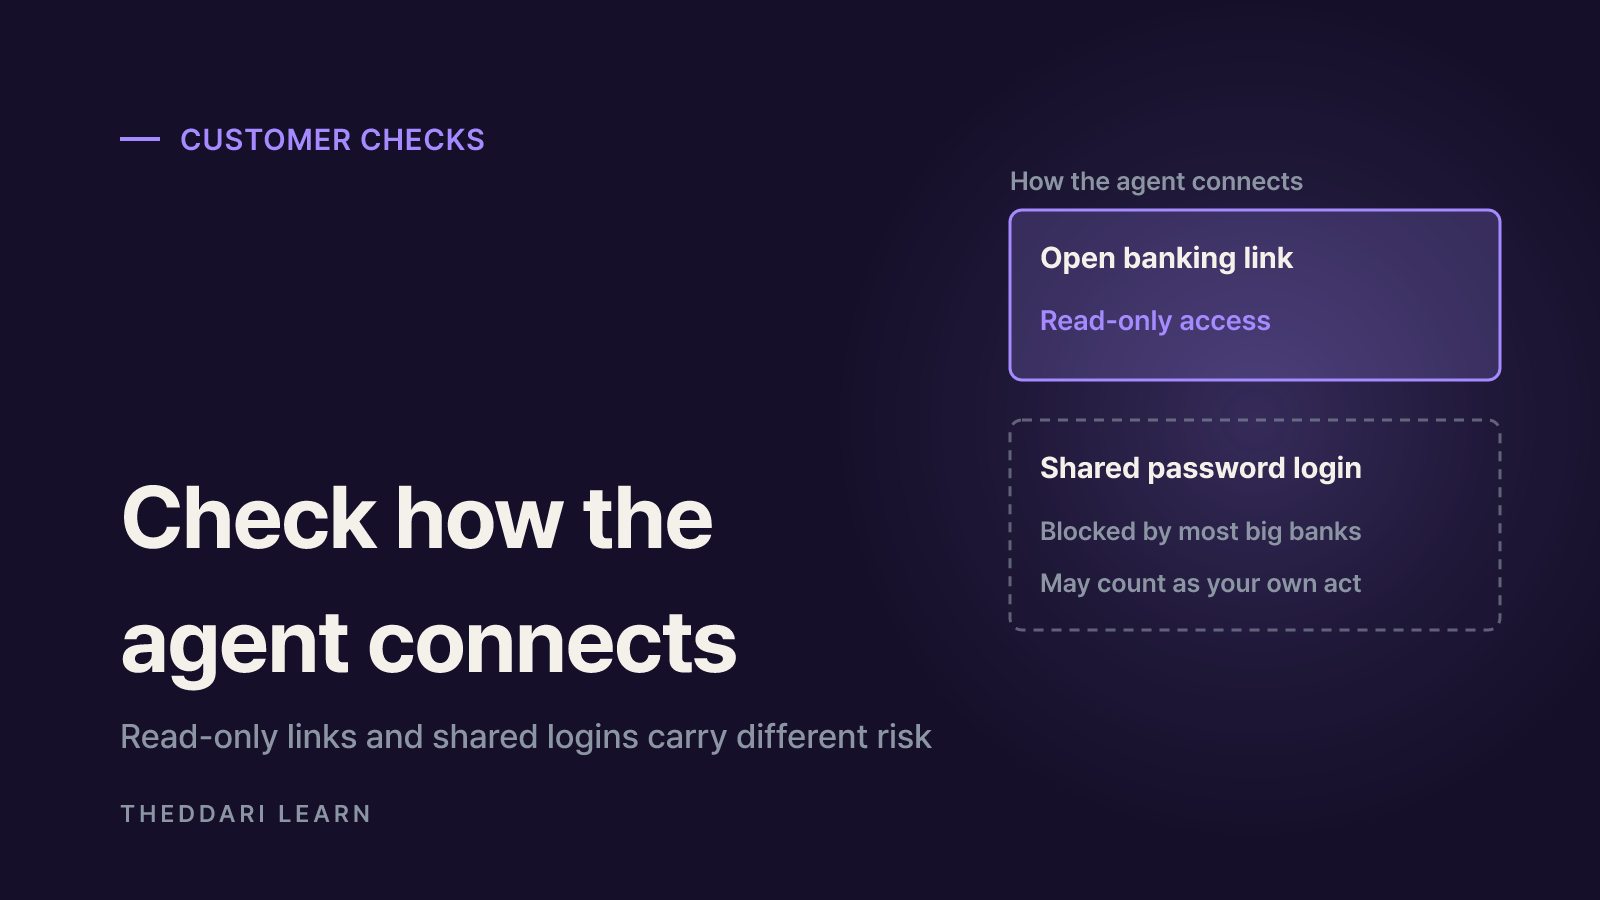
Bank controls ultimately shift risk onto customers who bypass them. Dimon said people using outside agents should understand there is a "liability transfer." Wells Fargo's online access agreement, quoted by American Banker, says transactions initiated by an agent you gave your credentials to are deemed authorized by you without further verification. The steps below reflect US bank practice; customers of banks in other countries should check their own terms.
- 1
Identify the connection type
Check whether the agent reads data through a bank-approved open banking connection or logs in with your username and password. Most large US banks now block the second method.
- 2
Read the agent clause in your terms
Look for new language about AI agents or third-party logins in your online banking agreement. Clauses that treat agent activity as your own can limit your options after a bad transfer.
- 3
Grant the minimum permissions
Let an agent check balances, but avoid giving it the ability to move money, pay bills or add payees. If you need it to buy things, consider a separate payment method with a fixed limit.
- 4
Turn on alerts
Enable alerts for logins, password resets and new payees so you notice unusual activity from an agent or an attacker quickly.
Bank executives often state agent policies on earnings calls, as JPMorgan and PNC did this quarter. Tracking upcoming bank earnings dates helps you catch policy changes from the source.
Open questions: agent identity and liability
Blocking is not airtight. According to American Banker, banks mostly stop agents that identify themselves, while agents running in Chromium-based browsers can mimic human typing and clicking. Fraud tools built around humans, such as device fingerprinting, behavioral biometrics and transaction profiling, lose power when an agent logs in from changing cloud devices. An American Bankers Association survey of more than 4,000 US adults cited in the article found 77% were concerned about giving an AI agent permission to move money or make payments.
Industry efforts are starting. Meta and Sierra introduced a protocol called Poppy for agents to identify themselves and obtain customer permission, with Bank of America and Wells Fargo as design partners, and Lead Bank proposed a liability framework for agent-led transactions that go wrong. Still, as of early November 2026 there is no agreed standard for verifying an agent, proving what a customer authorized, or assigning blame. Some expect a repeat of the screen-scraping era, when banks and aggregators eventually signed API and authentication agreements, but no timeline exists.
Bottom line: banks are answering outside agents with a read-yes, act-no permission split, and wrapping internal agents in audit logs and human approval. US model risk guidance still leaves agentic AI out of scope, while South Korea is building agent rules on top of a staff-accountability principle. For customers, the first checks are how an agent connects and what your bank's terms say about liability.